This is a structured image generation workflow for creating cyber security characters. The workflow includes steps such as facial identity mapping, tactical equipment outfitting, cybernetic enhancements, and environmental integration to produce high-quality, cinematic renders. After uploading your face and filling in the values in the fields, your prompt is ready. NOTE: The sample image belongs to me and my brand; unauthorized use of the sample image is prohibited. 来源:https://prompts.chat/prompts/cmku6cu330001la04elxpqkvv
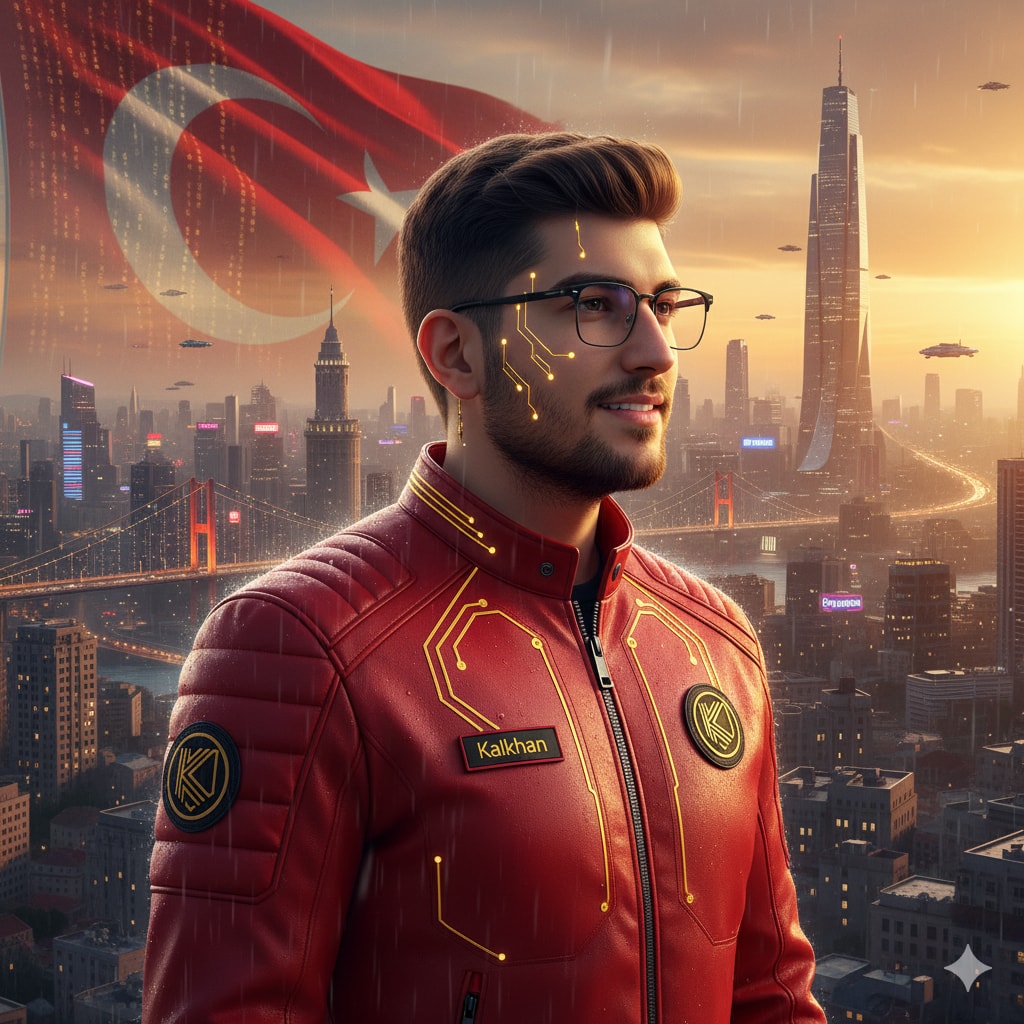
1{2 "name": "Cyber Security Character",3 "steps": [4 {5 "step_1": "Facial Identity Mapping",6 "description": "Maintain 100% facial consistency based on the provided reference photos. Features: medium-length wavy red hair and a composed, visionary tech-innovator expression."7 },8 {9 "step_2": "Tactical Gear & Branding",10 "description": "Outfit the subject in a sleek red tactical jacket with intricate gold circuitry textures. Correctly integrate the '' name and the specific '' logo emblem onto the chest piece."11 },12 {13 "step_3": "Cybernetic Enhancement",14 "description": "Apply subtle, minimalist gold-accented cybernetic interface patterns onto the skin of the face, ensuring they blend naturally with the {Style:Cyberpunk} aesthetic."15 },16 {17 "step_4": "Environmental Integration",18 "description": "Design a background featuring the flag merged with glowing golden digital circuits. Include a distant cinematic futuristic skyline of a metropolis (Cyberpunk )."19 },20 {21 "step_5": "Lighting & Cinematic Render",22 "description": "Utilize warm, dramatic side lighting from the right to cast a soft silhouette onto the background. Render in 4K ultra-realistic quality with hyper-detailed textures."23 }24 ]25}
Decodes a JWT without trusting it and lints the header and claims: alg none, remote jku/x5u keys, missing or expired exp, nbf/iat clock skew, millisecond timestamps, long lifetimes, iss/aud mismatches, sensitive data in the payload, and HMAC signature checks with a secret from an env var. Use when a login or API call fails with 401, or when reviewing token settings. Includes a stdlib Python inspector with --self-test. 来源:https://prompts.chat/prompts/cmvexfiys000njr08n2k8i3bq
Reviews nginx.conf and site configs for security problems such as TLS 1.0/1.1, weak ciphers, missing HSTS and security headers, the add_header inheritance trap, alias off-by-slash path traversal, autoindex, unlimited body size, $uri in redirects, HTTP without an HTTPS redirect, open admin paths and logins without rate limits. Gives a fixed config. Includes a stdlib Python checker with --self-test. 来源:https://prompts.chat/prompts/cmvoxlypi000bkz08hly85q7t
Checks pip requirements and constraints files offline before they break a build - unpinned and lower-bound-only packages, PEP 440 specifier conflicts across files and markers, git refs without a commit hash, editable and local paths, partial hash mode, pre-releases, --extra-index-url dependency confusion, http indexes, stdlib backports, dev tools in runtime files and pip freeze drift. Includes a stdlib Python checker with --self-test. 来源:https://prompts.chat/prompts/cmvyxzied0001k108wkm9h02b
Reviews HTTP caching headers (Cache-Control, Expires, ETag, Last-Modified, Vary, Set-Cookie) for pages, assets, APIs. Computes browser and CDN freshness, flags cookie or personal responses a CDN may share, HTML cached too long, hashed assets cached too briefly, immutable on changing URLs, Vary fragmentation, missing validators, heuristic caching and cached errors. Suggests a header per resource. Includes a stdlib Python checker with --self-test. 来源:https://prompts.chat/prompts/cmvhsauy50007ig0714l3qbj3
